Kluis
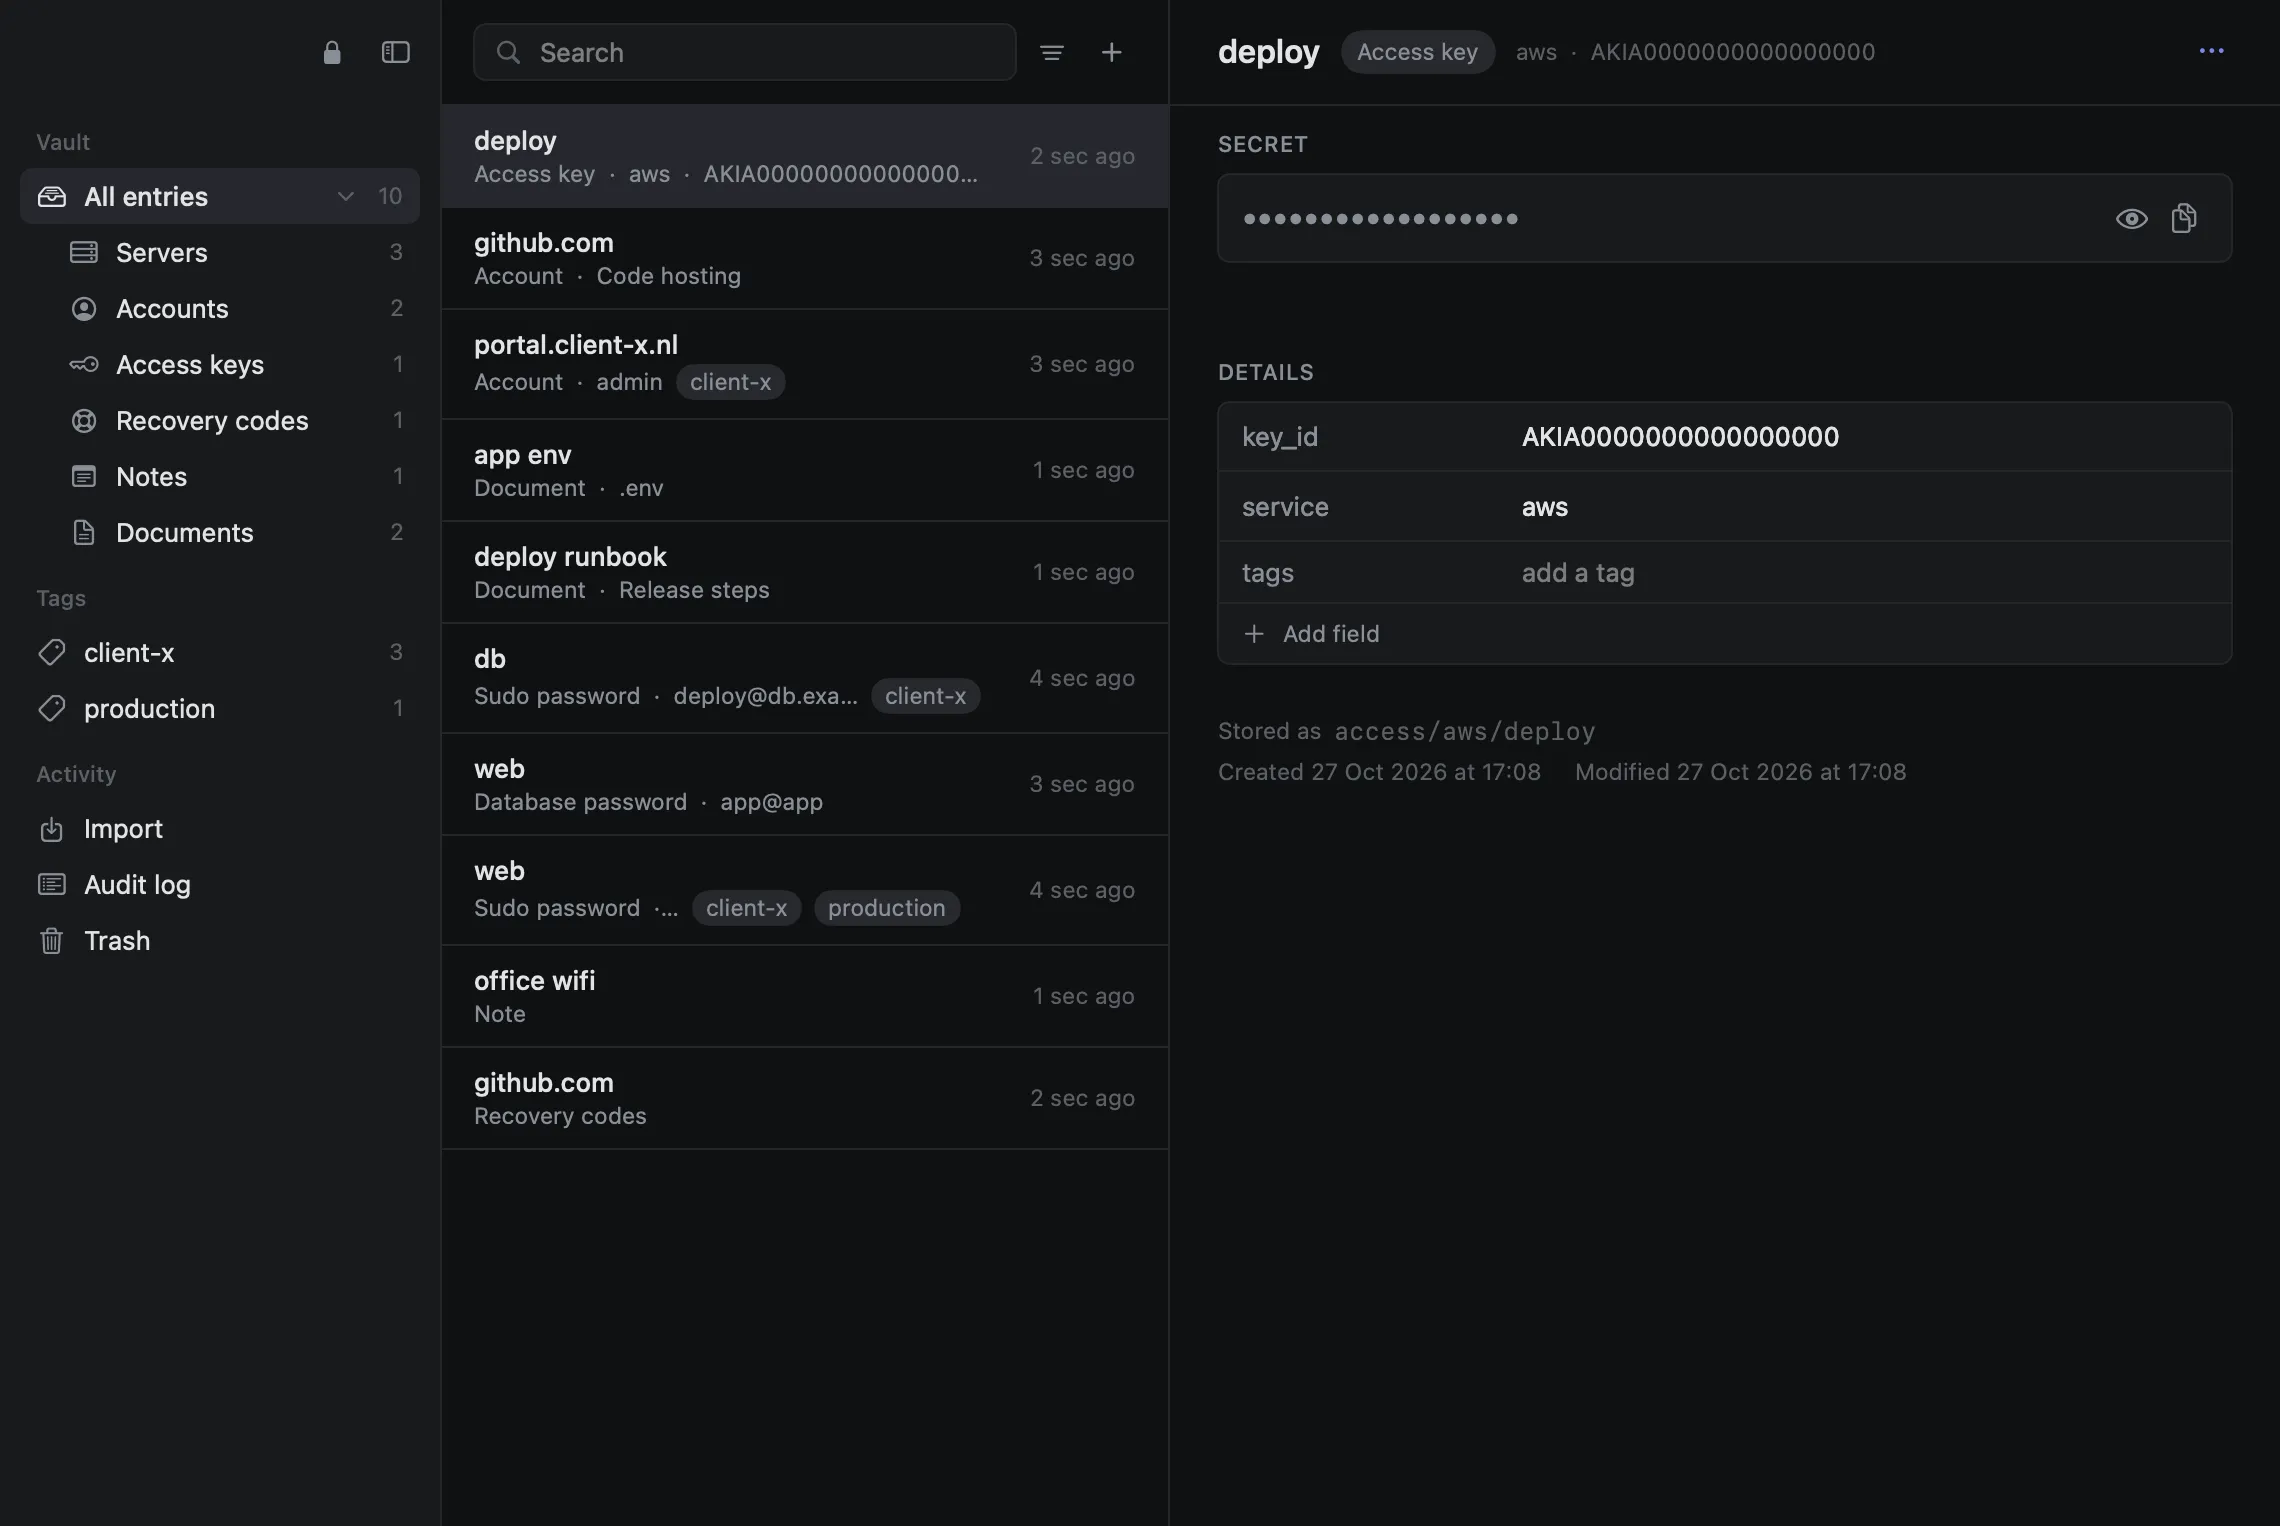
A password vault for the Mac. Keys in the Secure Enclave, Touch ID for every read, and AI agents that use a secret without ever seeing it.
- Made by
- Vagebond
- Type
- Own product
- Stack
- Swift, SwiftUI, Secure Enclave
The challenge
AI agents need secrets to run commands, but an agent that can read a secret can leak it.
Our solution
Kluis gives the secret to the command, not to the agent. A policy limits the entries and commands, and every read asks for Touch ID.
Touch ID for every read
Secrets are encrypted to a key in the Secure Enclave. Names use a second, silent key, so you can search without a prompt. The window stays out of screen captures.
Same vault, no window needed
The kluis command reads the same vault. It types sudo passwords over ssh and keeps private keys off the disk. Every read asks for Touch ID, with the entry and the purpose in the prompt.
# The sudo password over ssh, after Touch ID
kluis ssh web

# A secret for one command, gone when it ends
kluis run -e TOKEN=api/github -- gh

# A new sudo password, set on the server and proven
kluis rotate hosts/web/sudo
Safe for AI agents
Agents run commands with a secret, but they never read it. A policy says which entries and commands they may use, and the audit log shows every use, by you or by an agent.
Documents
Runbooks, .env files, YAML and JSON, encrypted like a password. Markdown gets a formatting editor, the rest gets a code editor.
A page for the day you are gone
Kluis splits the backup key between two to five trusted people with SLIP-39, a public standard. Each person gets one printed page with the words, a code and the steps. One page alone opens nothing.
Stack
- Swift
- SwiftUI
- Secure Enclave
- age
- Sparkle